Open Source Authentication

Forge Auth

Central authentication for the BlueForge ecosystem. Single sign-on across all your apps — plus organizations, tenancy, device-flow API keys, and org-level billing, resolved from one identity platform.
A glowing shield with a keyhole at its centre, linked by threads of light to a ring of app tiles: one BlueForge identity signing in to every app.

Everything You Need for Auth

Identity, tenancy, and billing for the whole BlueForge portfolio — one platform, nothing extra to run.

Four glass blocks of member nodes, each wired to one central shield.

Organizations & Tenancy

Multi-tenant identity for every BlueForge app: organizations with owners, admins, and members, a personal org for every user, and invitations — all resolved from a single session.
A single glowing key radiating beams to a ring of app tiles.

Single Sign-On

One OAuth flow shared across the whole ecosystem. Google, GitHub, and Gitea credentials live here and federate to each app — and Forge Auth is the OAuth authorization server for the fleet's MCP servers, so an AI tool server reuses the same account as every other app.
A laptop terminal passing a key along a dotted arc to a phone that confirms it.

Device-Flow API Keys

Desktop CLIs log users in once, then issue user-bound keys for unattended calls. Sibling apps resolve any key back to its owning user through the /api/v1/users/resolve verifier.
A row of server modules on a lit track, handing glowing tokens to one another.

Federation Service Accounts

Scoped service accounts: mint them through the admin API, exchange them for short-lived tokens, and let the consuming service resolve them — no shared human credentials between services, and an organization can narrow a grant but never widen it.
A glass payment card beside three rising tier pillars, the tallest marked with a check.

Plans & Entitlements

Stripe checkout, portal, and webhooks attach platform plans at the org level, so apps read plan entitlements (like financials.apps.max) instead of running their own billing. Billing runs against Stripe's test ledger while live keys are provisioned.
A central hub sending envelopes of light along curved paths to surrounding nodes.

Webhook Events

HMAC-signed organization.*, member.*, invitation.*, service_grant.*, subscription.* and account.* events fan out to every connected app, with idempotency keys and retries — so mirrors stay fresh without polling.

See it in action

Six real screens from a running build — the organization page, its service grants, and the per-app admin console. No mock-ups.
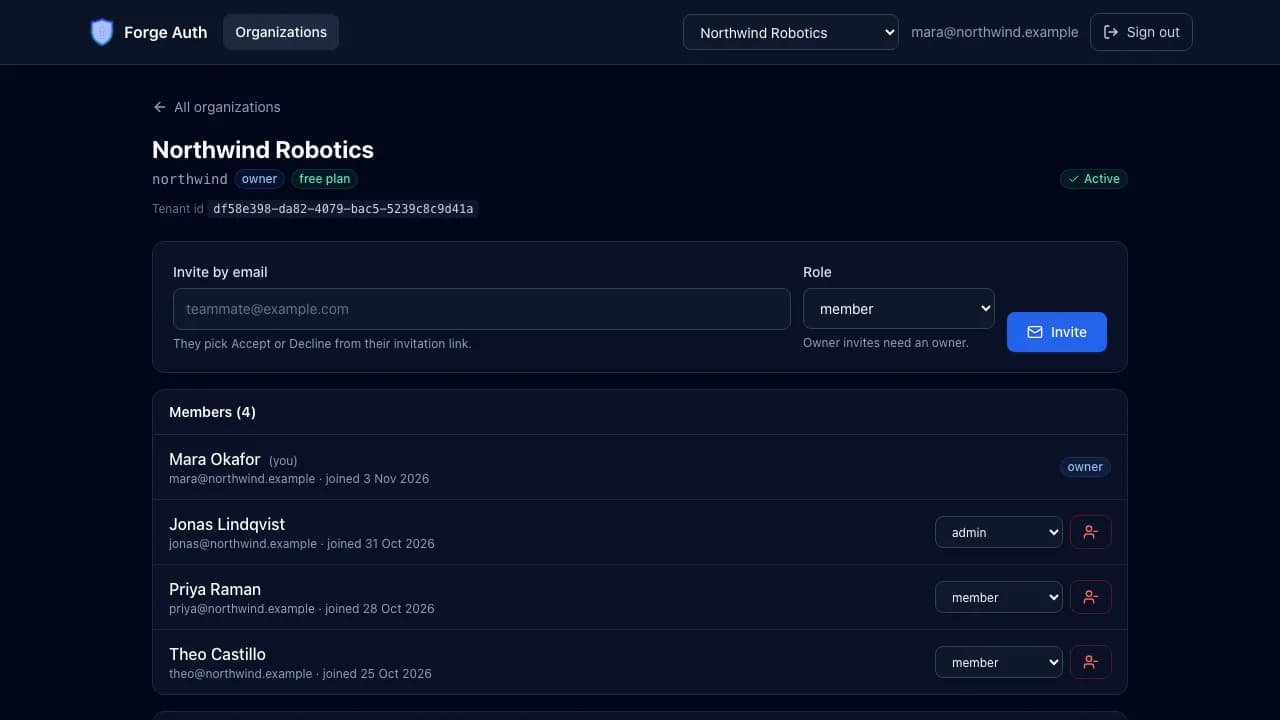
The Northwind Robotics organization page in Forge Auth listing four members with their roles, an invite form and a pending invitation.
Organizations with owners, admins and members, and invitations
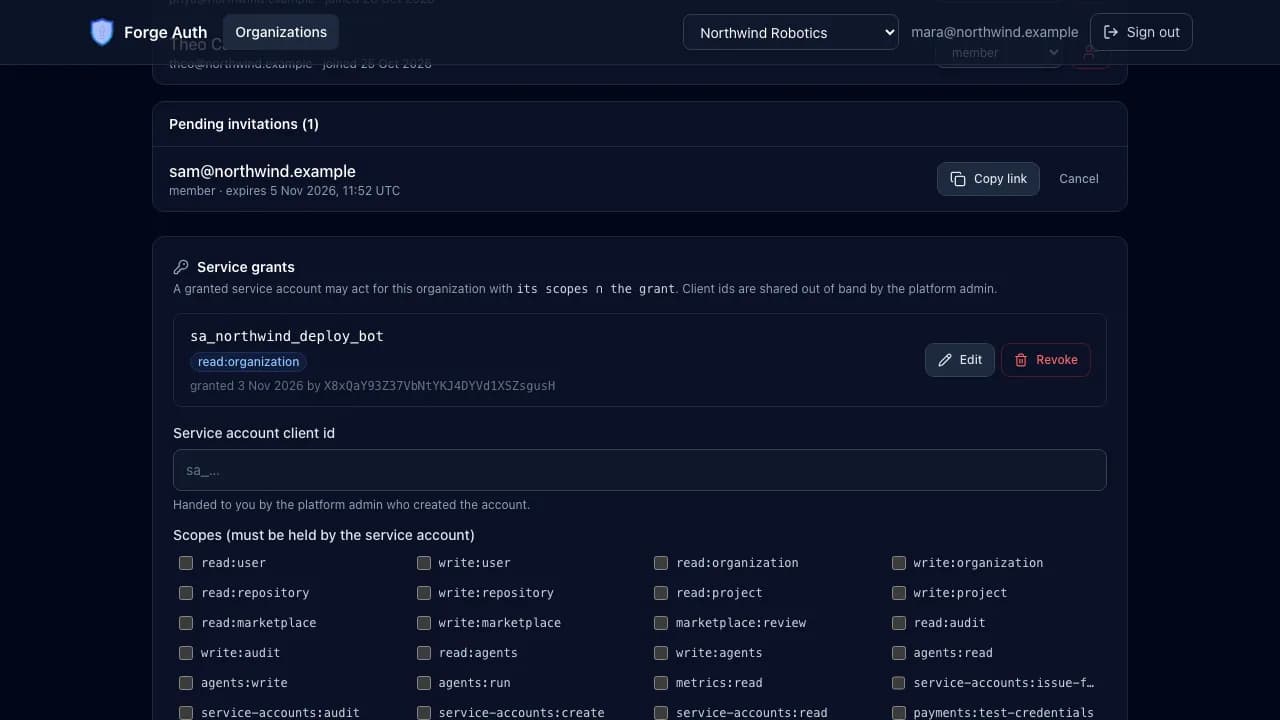
The service grants card on the Northwind Robotics organization page, listing the Northwind deploy bot service account and the read:organization scope granted to it.
Service accounts granted access to an organization, with the scopes each one holds
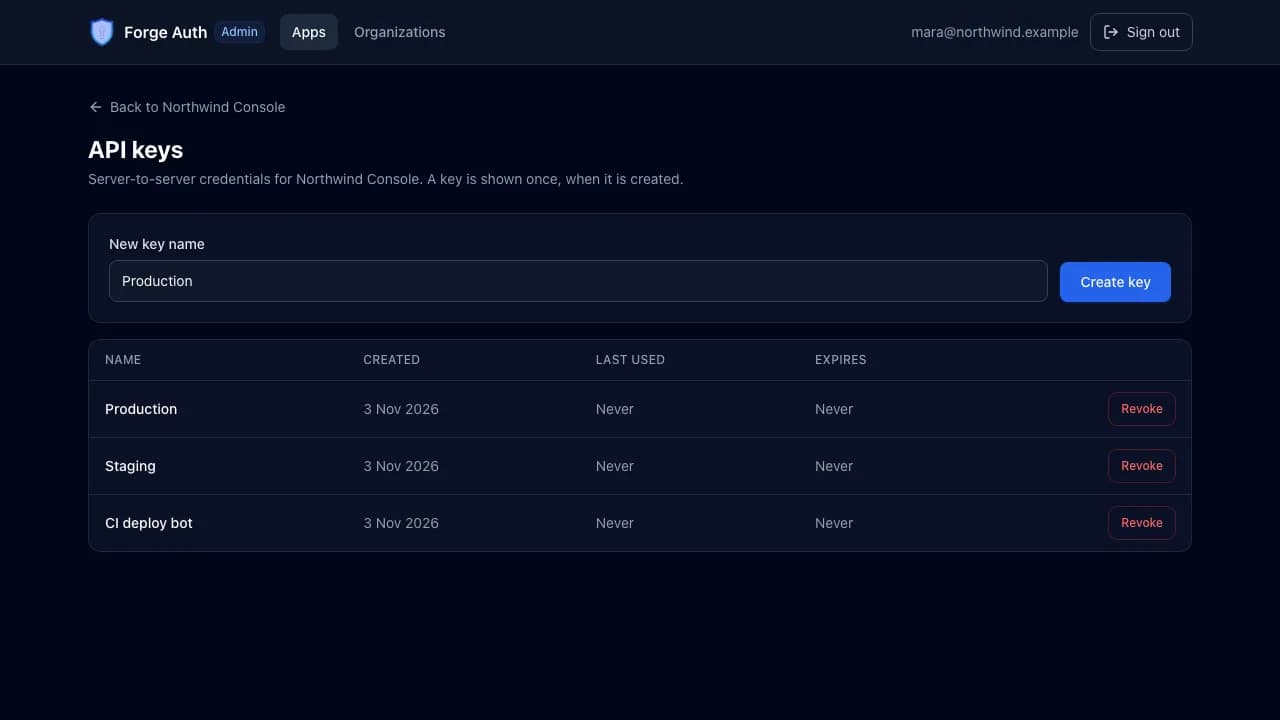
The API keys page for the Northwind Console app in the Forge Auth admin dashboard, listing Production, Staging and CI deploy bot keys.
Per-app API keys, created and revoked from the admin console
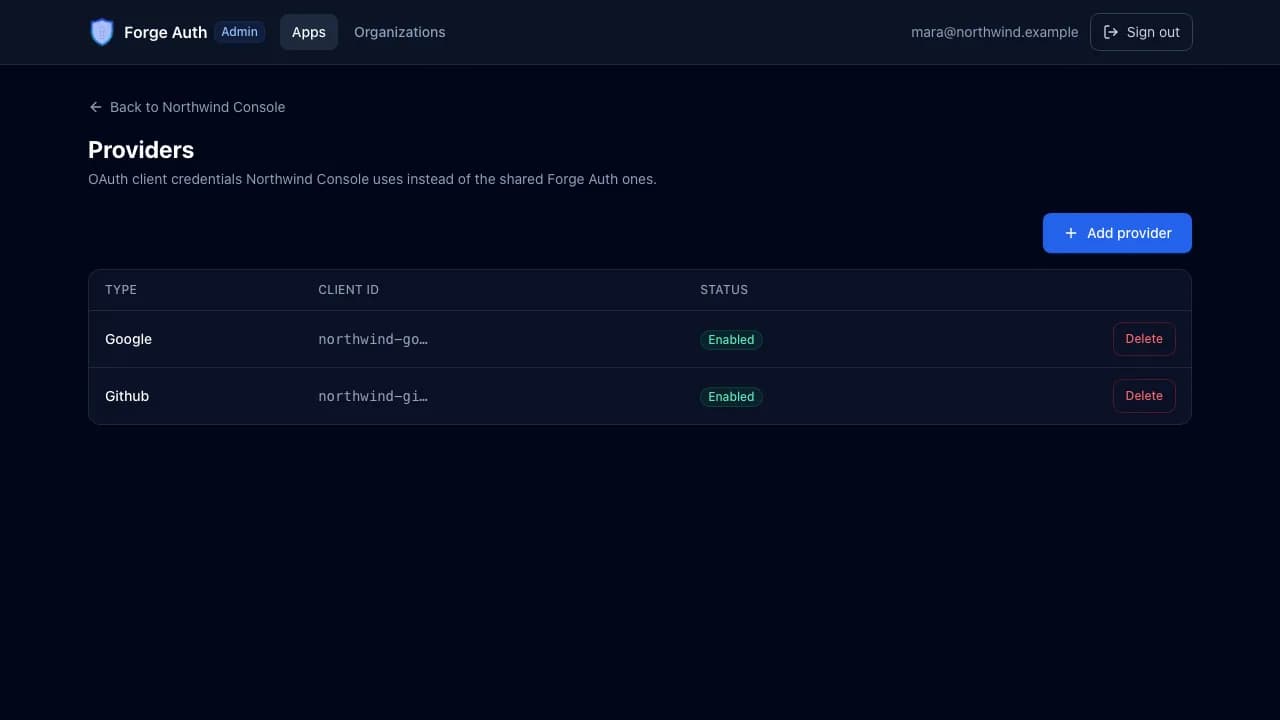
The providers page for the Northwind Console app in the Forge Auth admin dashboard, listing the Google and GitHub providers enabled for it.
OAuth providers per app, so a tenant can use its own client credentials
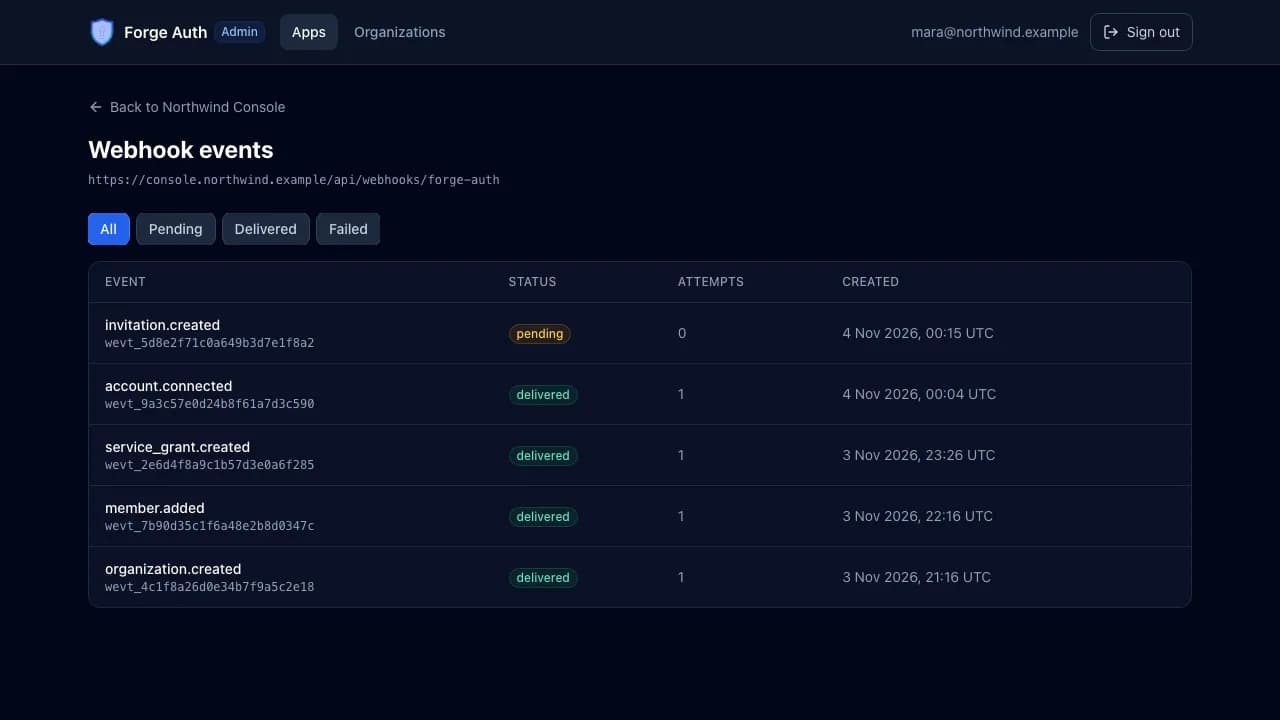
The webhook events page for the Northwind Console app in the Forge Auth admin dashboard, listing organization.created, member.added, service_grant.created, account.connected and invitation.created events with their delivery status.
Every webhook event delivered to an app, with its delivery status and retry count
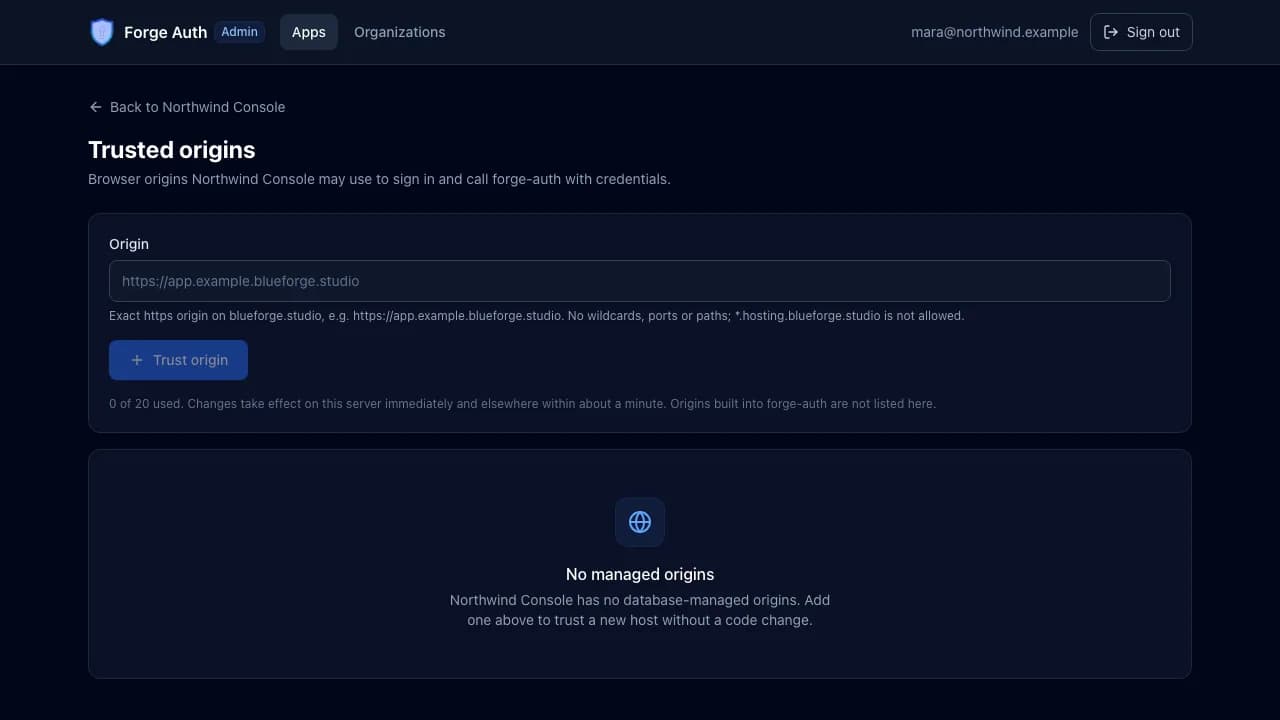
The allowed origins page for the Northwind Console app in the Forge Auth admin dashboard, listing the console.northwind.example callback origin.
The callback origins an app may return to

Simple, Transparent Pricing

Start free, upgrade when you need more. Pay yearly and get two months free.

Free

$0/forever

For personal projects and prototypes.

  • Up to 1,000 monthly active users
  • 1 application
  • Google & GitHub OAuth
  • Community support
Get Started

Basic

$19/per month

For side projects and small apps going live.

  • Up to 1,000 monthly active users
  • Up to 10 applications
  • API key management
  • Email support, 72-hour response
Get Started
Most Popular

Pro

$49/per month

For growing products and small teams.

  • Up to 10,000 monthly active users
  • Up to 50 applications
  • 1 seat included, up to 10 ($15/extra seat)
  • Webhook events
  • Email support, 24-hour response
Get Started

Team

$99/per month

For teams running production apps.

  • Up to 50,000 monthly active users
  • Up to 200 applications
  • 5 seats included, up to 50 ($15/extra seat)
  • SAML & OIDC SSO (coming soon)
  • Priority email support, 8-hour response
Get Started

Need unlimited users, an SLA or on-premise deployment? Talk to us about Enterprise.

Ready to Secure Your Apps?

Set up centralized authentication for your entire organization in minutes.